SSO (Single Sign-On) Options in Korbyt
This article reviews the ways to configure SSO and user management in Korbyt
Written By Ed Kinne
Single sign-on (SSO) for Korbyt CMS enables you to use your existing corporate user/password details when logging in to the Korbyt CMS. It eliminates the need to keep passwords updated in the CMS and simplifies access for users already logged in to their corporate network.
Korbyt supports multiple options for SSO and User Management
Azure AD Integration: Korbyt imports users from your Azure AD groups and keeps them in sync.
SAML 2.0: Users sign in through your identity provider (IdP), and Korbyt creates their CMS account the first time they log in.
In the CMS, SSO Integration settings can be found
In the Sidebar Nav Menu
In the Integrations section, click Single Sign-On
Then click on the SSO type button (Azure AD, or IdP for all other SAML options)
In the Mega Menu
In the Advanced section, click on Directories
Then click on the SSO type button (Azure AD, or IdP for all other SAML options)
Review the specific section for your deployment (you can select a service using the navigation menu on the right.
Azure AD Integration
Korbyt Anywhere provides integration with Azure AD for secure and scalable user management and single sign-on, allowing a customer's employees to log in to the Korbyt Anywhere CMS using their Azure AD credentials.
This process will require configuring both your Korbyt tenant and your Microsoft Azure services. Your IT department, as well as Korbyt Professional Services, will likely be involved in the process.
This document provides high-level insight into the process steps.
There are three main steps in the setup process:
Granting Access: In your MS Azure service, you must grant Korbyt Anywhere access to the desired Azure AD groups
In Azure – Registering an app on the Azure app registration portal
In Azure – Confirming permissions for Microsoft Graph on the app
Microsoft Graph API permissions are required for integration with Azure AD
This article lists the specific Microsoft Graph API Permissions Required by Korbyt
In Azure – Obtaining Administrator consent
In Azure – Generating a Client Secret
Record the details from these steps, as they will be used in Korbyt to create the connection
Importing CMS Users Through Azure
CMS Users are those who will log in to the web portal to manage the platform.
Further down this article you will find details about importing End Users, those that will only be logging into the Desktop or Mobile Applications
If someone is both a CMS and End User they will need to be imported through both setups
Importing Users: Inside Korbyt Anywhere, set the information so that Korbyt can automatically create a corresponding CMS user for each employee it detects in the customer's designated Azure groups
In Korbyt – Enter User Import Parameters
In the Sidebar Nav Menu, open or hover over Integrations, then select Single Sign-on
In the Classic UI, open the Mega Menu; in the Advanced section, select Directories
On Directories, select if you are using Azure AD or a different IdP
For IdP
Turn on the Services you wish to use
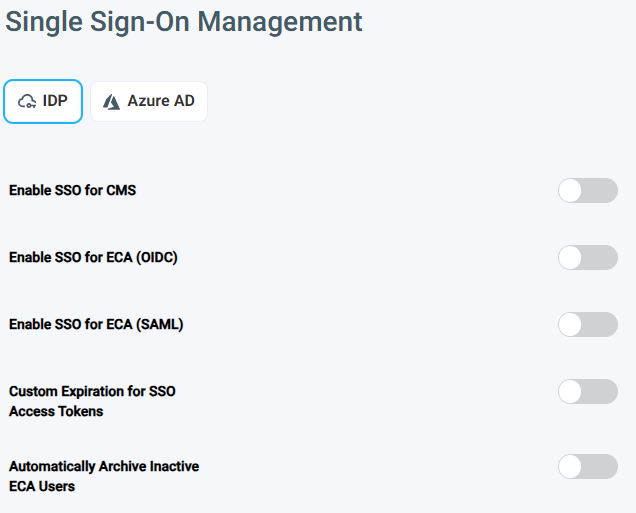
Then configure the information required for that service
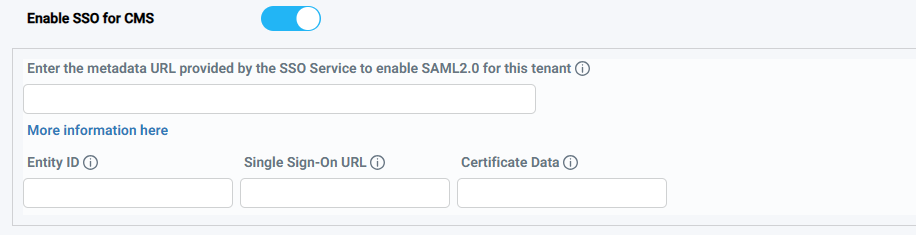
Enable SSO for CMS
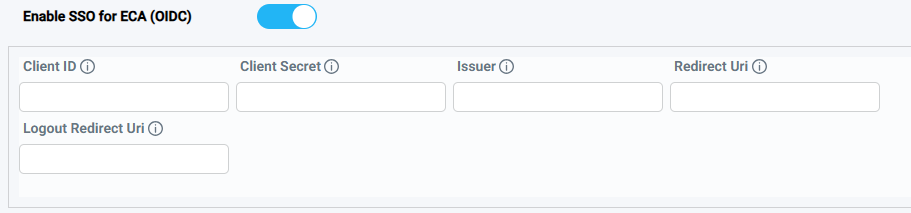
Enable SSO for ECA(OIDC) - Korbyt Mobile and Web
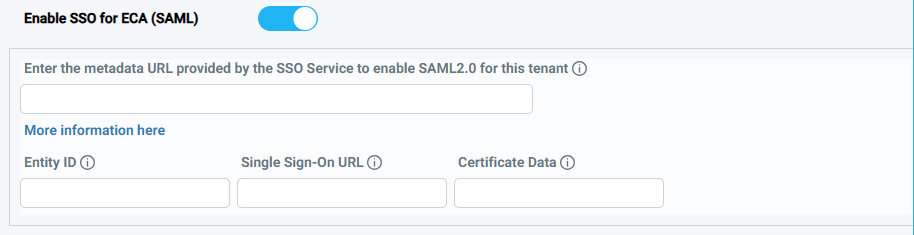
Enable SSO for ECA (SAML) - Korbyt Mobile and Web
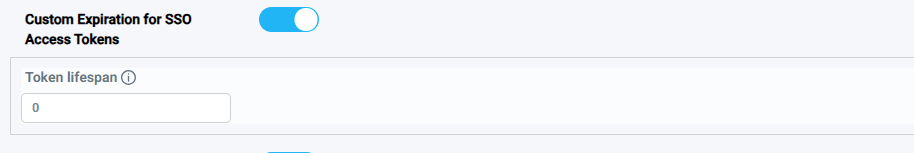
Customer Expiration for SSO Access Tokens
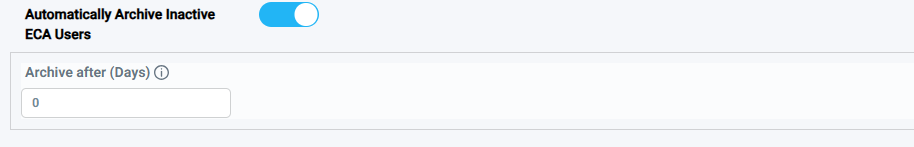
Automatically Archive Inactive ECA Users - Korbyt Mobile and Web
For Azure AD
Click the pink +Add New Azure Users button and enter the details you established in the first steps
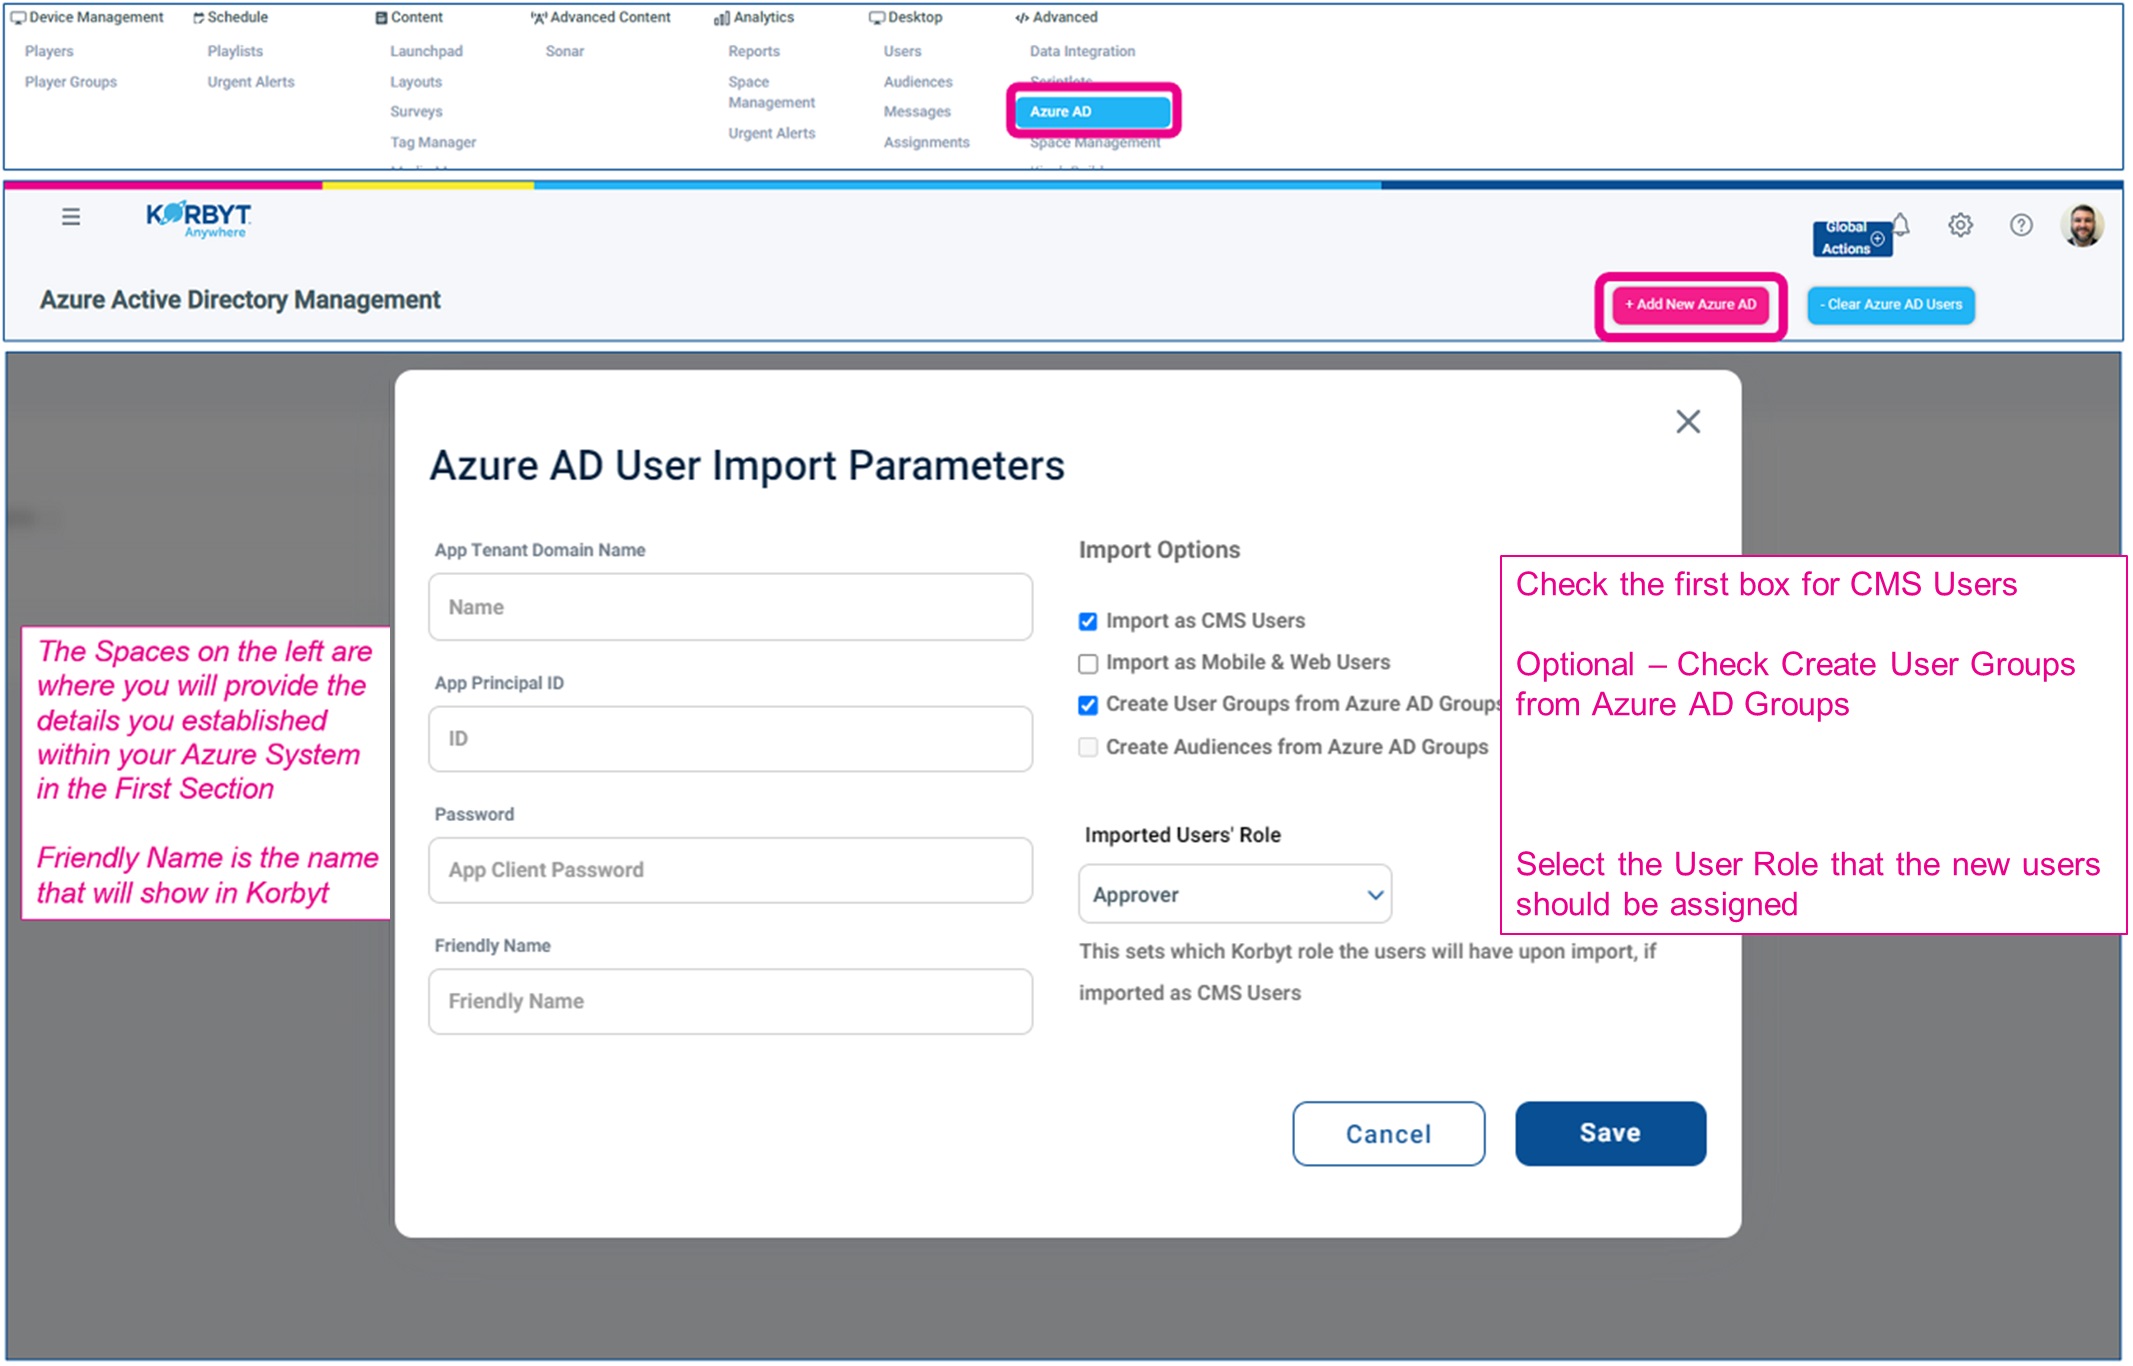
Click Save
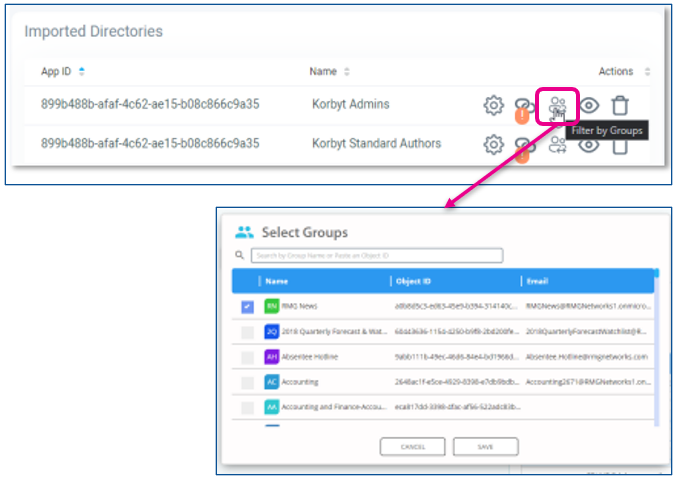
In Korbyt – Filter By Group
If specified, the import process will only add users that are members of selected groups. This can be helpful if you have a large number of users and you only want to import a subset of those users
In the Azure Menu, use the Action to select Filter By Group
Now this connection is established, Azure AD and Korbyt will communicate periodically to match the users that should be in Korbyt based on the information in your Azure AD
Employee Login: Once the import is processed and complete, an employee will be able
to log in to Korbyt Anywhere using their Azure credentials
Import End Users Through Azure
End Users are those who only log in to the Desktop or Mobile & Web platforms and do not access the Korbyt tenant to adjust settings.
If someone is both a CMS and End User, they will need to be imported through both setups.
Importing Users: Inside Korbyt Anywhere, set the information so that Korbyt can automatically create a corresponding CMS and/or Desktop or Mobile user for each employee it detects in the customer's designated Azure groups
In Korbyt – Enter User Import Parameters
In the Sidebar Nav Menu, open or hover over Integrations, then select Single Sign-on
In the Classic UI, open the Mega Menu; in the Advanced section, select Directories
Click the pink +Add New Azure Users button and enter the details you established in the first steps
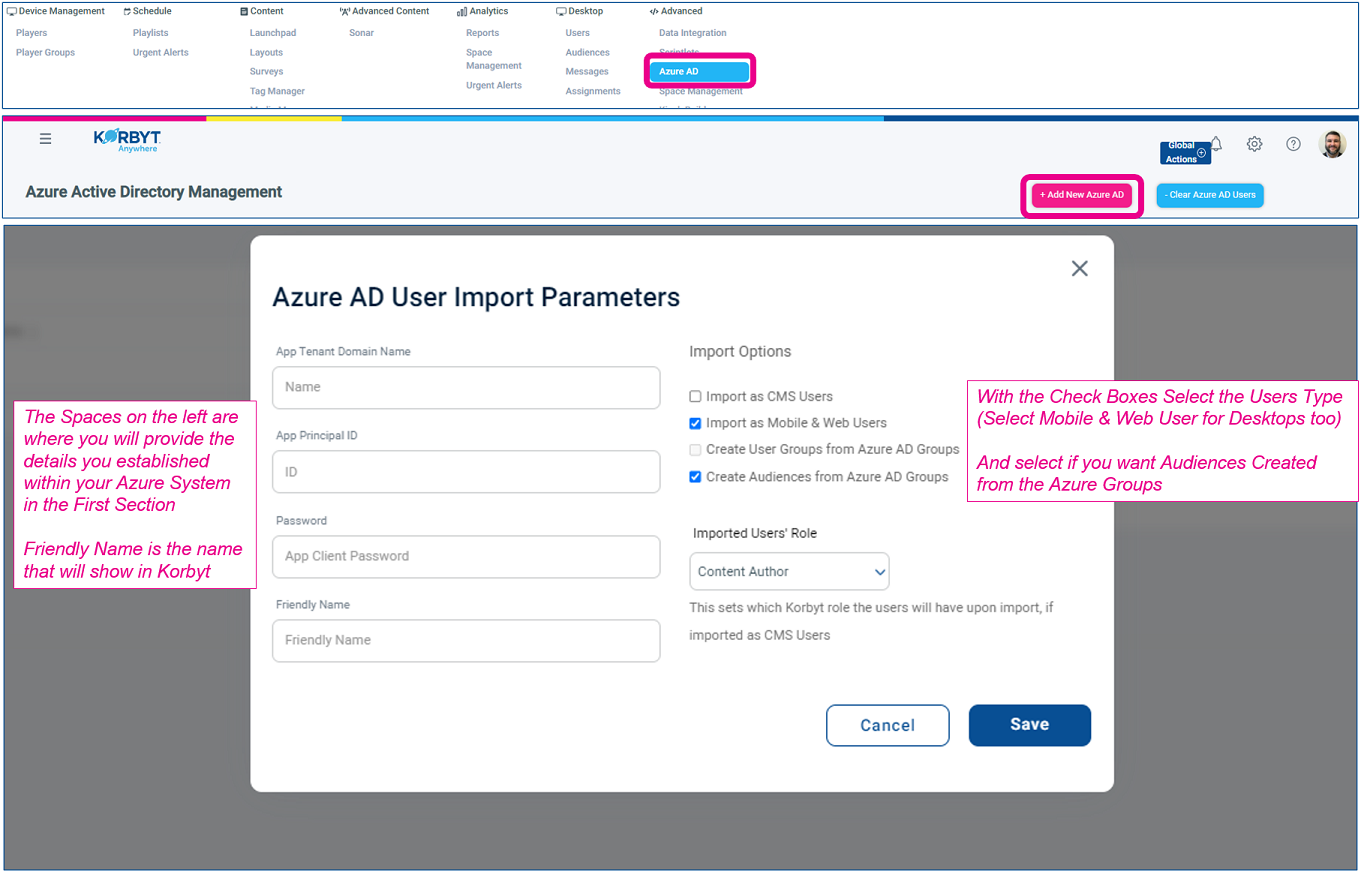
Click Save
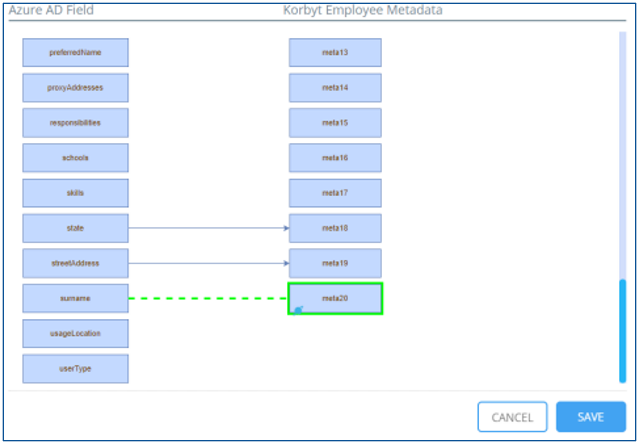
In Korbyt – Map Azure Fields to Employee Metadata
This will allow you to select the Azure AD fields you would like to make part of the employee record in Korbyt
In Korbyt – Filter By Group
If specified, the import process will only add users who are members of selected groups. This can be helpful if you have a large number of users and you only want to import a subset of those users
In the Azure Menu, use the Action to select Filter By Group
Now that the connection is established, Azure AD and Korbyt will communicate periodically to match the users that should be in Korbyt based on the information in your Azure AD.
Employee Login: Once the import is processed and complete, an employee will be able to log in to the Korbyt Mobile or Desktop applications using their Azure credentials
SAML 2.0 Integration to Manage CMS Users
IdP vs SP
Korbyt supports SAML 2.0 Identity Provider (IdP) initiated SSO.
This is where the user logs in to the IdP, so is validated as part of that login, and all SSO is then handled by the IdP
Korbyt also supports SAML 2.0 Service Provider (SP) initiated SSO.
This is where the user logs in by navigating to their specific login URL to fire the SSO event to the customer's identity provider.
The URL will be formatted as https://delivery.korbyt.com/saml2/login, for example
Configuring Korbyt for SAML 2.0 SSO
Korbyt expects the following values from the IdP:
This integration is ultimately facilitated by an exchange of metadata between Korbyt and your IdP.
The Korbyt SAML2 metadata file that you provide to your identity management provider can be configured in the format below. The server FQDN will be unique to your server/tenant.
http(s)://<server FQDN>/saml2/metadata
For example, https://<your Korbyt subdomain>.korbyt.com/saml2/metadata
The example below is taken from a Korbyt demo hybrid tenant
The example below is taken from a Korbyt demo hybrid tenant
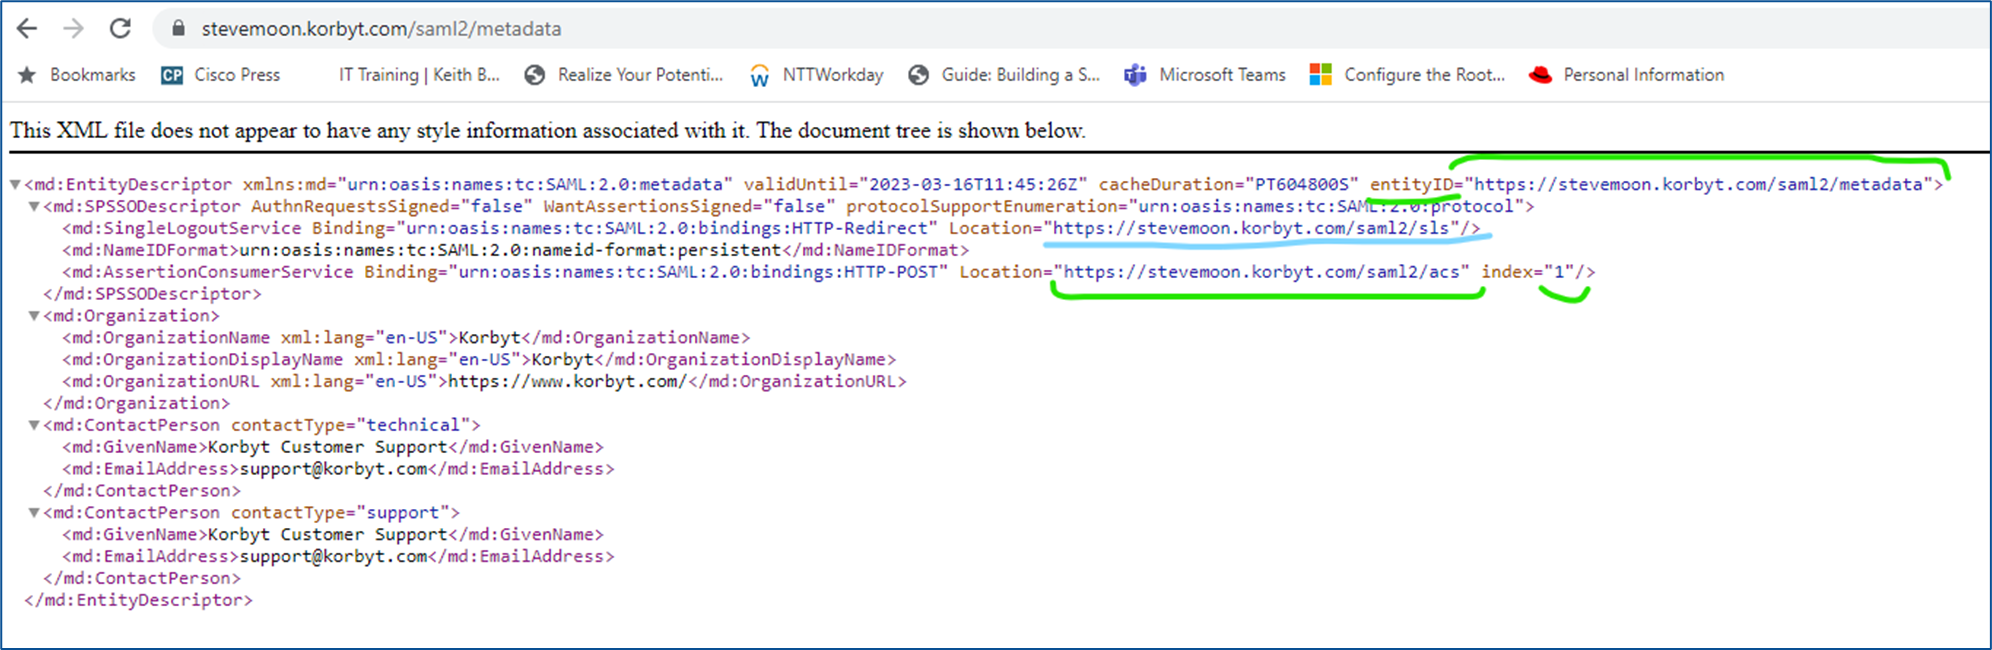
The output of the browser call is the XML file itself in readable form. You are interested in three entries, as well as an optional entry –
“entityID” – in this example = https://delivery.korbyt.com/saml2/metadata
“Assertion consumer service URL” = https://delivery.korbyt.com/saml2/acs
The ACS “index” = 1
Single Logout Service (optional) = https://delivery.korbyt.com/saml2/sls
If manually entering these values, click the edit “pencil” next to Basic SAML Configuration and enter the values as seen in the XML file in the browser window.
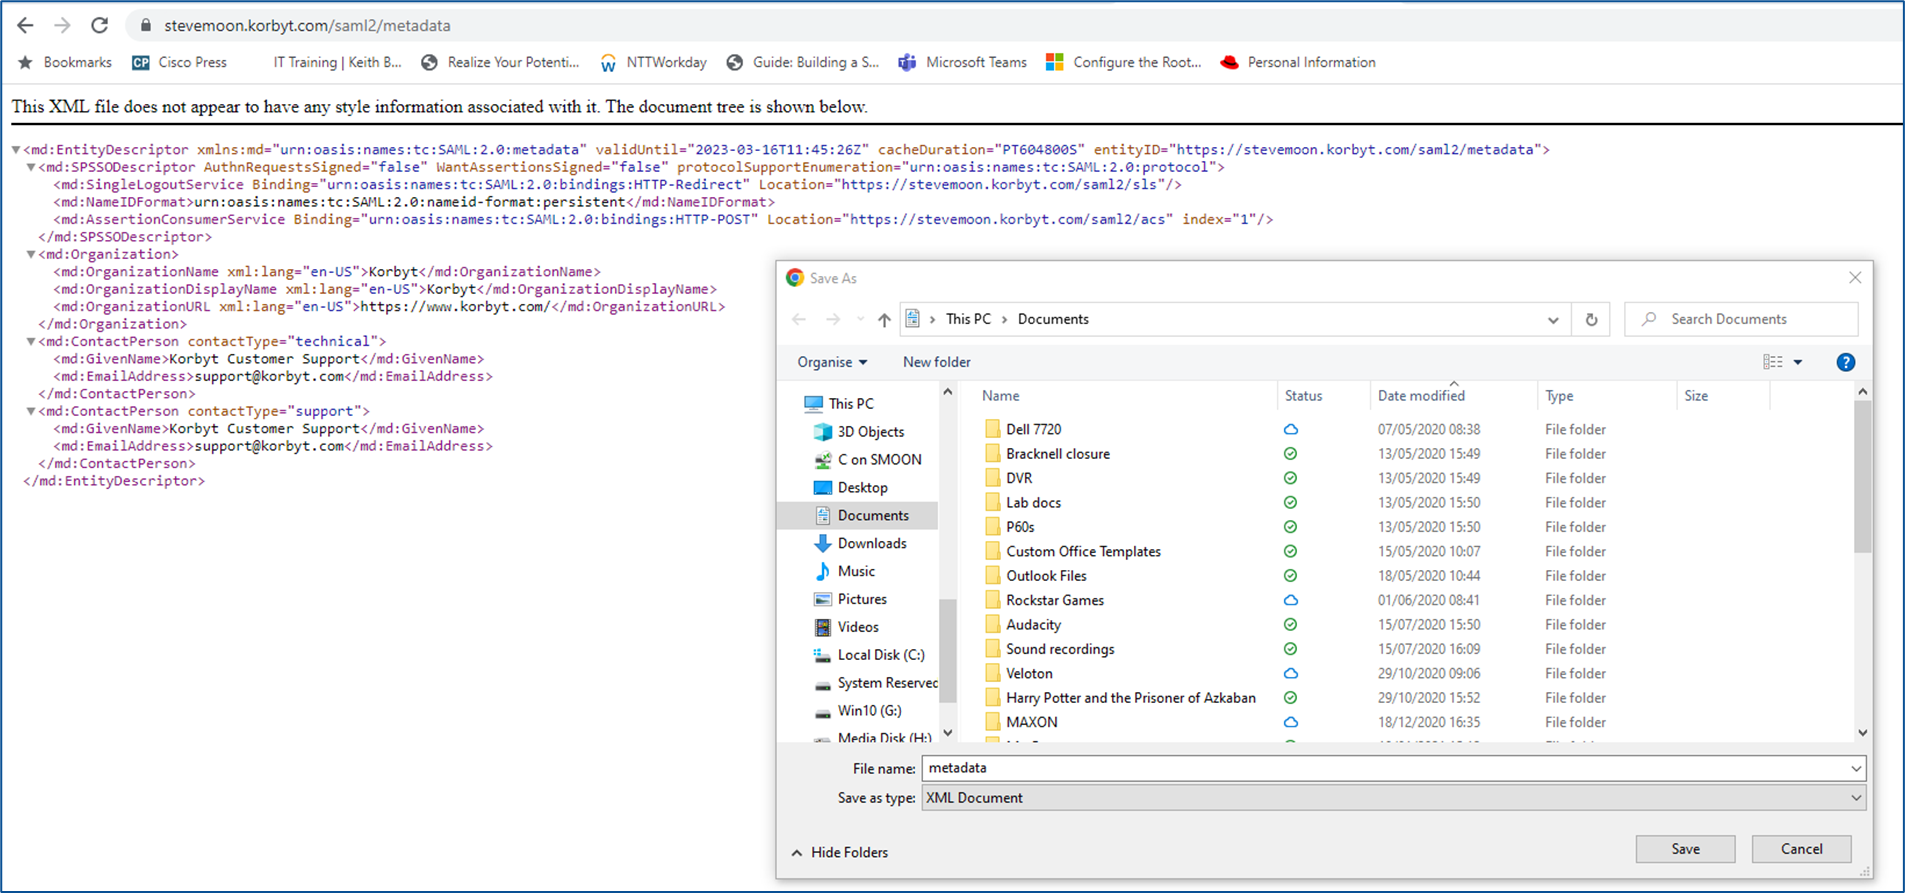
If uploading the XML file, save it from the browser session by right-clicking anywhere within the main browser window, selecting the "Save as" option, and then saving the XML file to a suitable location.
Provide your IdP Metadata URL to your Korbyt representative to configure your tenant for SAML SSO.
Note: Making the metadata available via URL is preferable if the values/certificates are going to be rotated or changed often
Note: If the IdP is MSFT Azure, the correct URL to provide is the Metadata Federation XML URL, but make sure that it is the full URL with the APP ID query string on it.
IdP needs to provide the following values in the SAML2 assertion –
FirstName
LastName
Email
Role
Groups (optional)
Tenant (optional)
We need to provide these values using the exact wording for each value as shown above, ie we need an assertion value named “FirstName” and one named “Email”, so we must ensure that the assertion info coming from your IdP is named in the format used by Korbyt.
The syntax of these 5 values can be uppercase or lowercase, but must be exactly the characters given above (ie no spaces). The internal SSO code of the server is able to handle uppercase, lowercase, or a mixture of the two, but the actual characters used must match those shown above. The code snippet below also shows the syntax as used for these 5 values.
Now that you have your SAML claims set with the correct name for Korbyt SSO, you need to ensure the correct values for those claims are being provided by your IdP
Role Claim
For the Role claim, Korbyt has 6 roles, and the table below shows the value you must include in the claim to match each role. For a breakdown of the roles and their abilities, see Content Managers (CMS Users) Roles And Abilities
Note: that these values must be entered exactly as shown in the table below.
If you do not provide a “Role” claim, or enter an invalid value compared to the table above, the user will be given the role of Content Author by default.
Groups Claim
For the Groups claim, the value sent in the “claim” must exactly match any existing User Groups that are already created on the Korbyt platform. For more info on creating user groups, see, How To Manage CMS Users And User Groups
New groups cannot be created via the SAML Groups claim. If the value in the Groups claim does not exactly match an existing User Group, the user created on the fly is not placed in a group and has no group membership. Multiple groups can be sent in the claim, with each group name separated from the others by a comma.
An example of a completed claim is below, where static values have been entered in the Role and Groups claim, which are usually dynamically provided via your IdP.
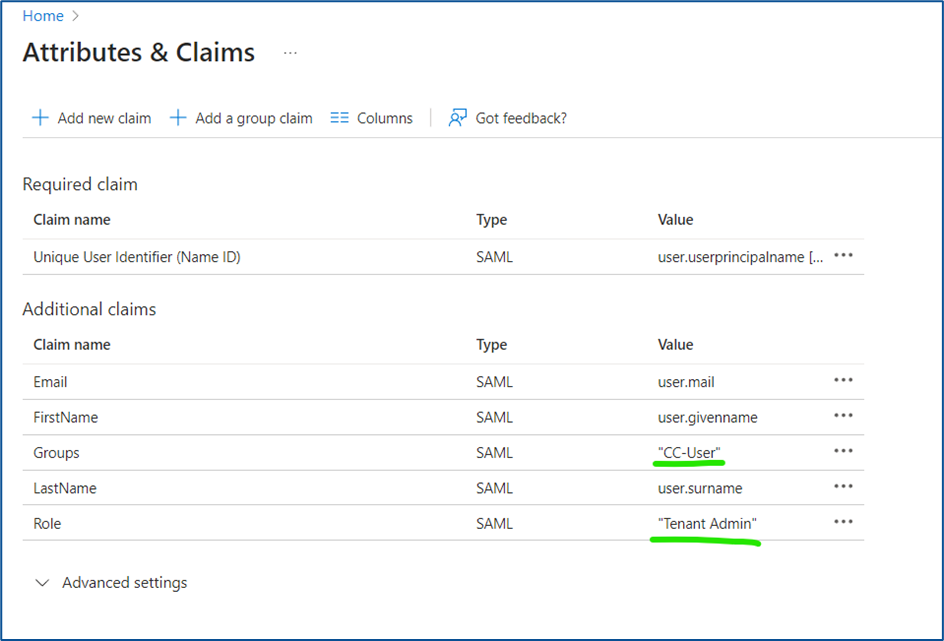
Once you have your attributes and claims set up, you should be ready to generate your metadata URL from your provider and enter it into your Korbyt tenant.
This document does not go into generating the metadata url so please consult your provider documentation or administrator for help with that process.
Set up Your IdP Metadata URL in Korbyt CMS
In the Sidebar Nav Menu, open or hover over Integrations, then select Single Sign-on
In the Classic UI, open the Mega Menu; in the Advanced section, select Directories
Click the IDP button
Then toggle on Enable SSO for CMS
Enter the metadata URL provided by your identity provider
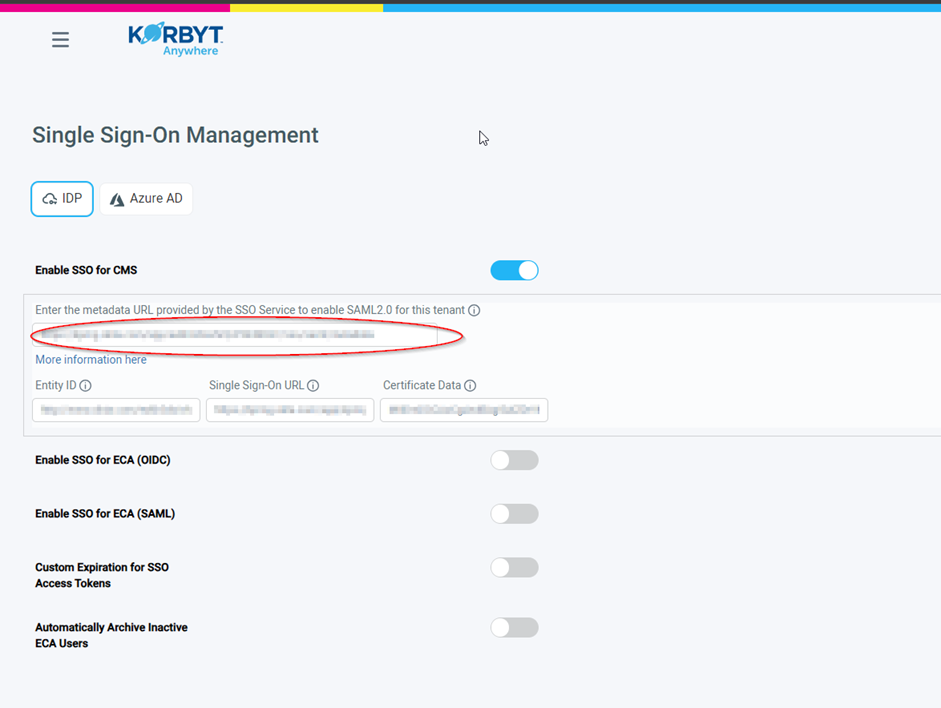
Korbyt will automatically query the metadata URL and fill in the Entity ID, SSO URL, and Certificate Data fields
Click Save
You should now have the correct information set in Korbyt and being entered into the SAML2 claim that will invoke SSO on the Korbyt server when the user clicks on the "Korbyt" app from their app tray or visits the login URL.
Was this helpful?
Still need help? Share an idea